Imported Certificate Replaced by Self-Signed Certificate
Symptom
This issue is usually discovered through a process similar to the following:
- You have successfully imported a custom certificate as your WSUS signing certificate and distributed it throughout your environment to facilitate deployment of third-party patches.
- You suddenly find that recently published updates are failing with an error related to the signing certificate not being trusted.
- You investigate and find your signing certificate is now set to a WSUS self-signed cert instead of your custom one.
- You re-import your certificate and republish affected patches.
- The next time you publish and deploy patches, you find the same issue again.
Cause
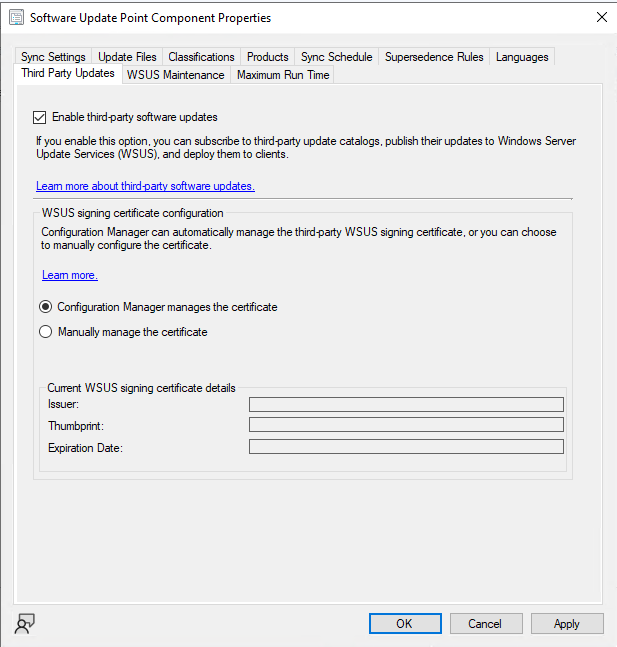
This issue is almost certainly caused by a specific configuration within the Software Update Point(s) properties in Configuration Manager when the 'Enable third-party software updates' option is checked under Administration > Site Configuration > Sites > Right-click the site > Configure Site Components > Software Update Point > Third-Party Updates. If the 'Configuration Manager manages the certificate' option is checked as below, this means that Configuration Manager will check the signing certificate with every WSUS sync, and if it is not a WSUS self-signed certificate, it will replace it with a self-signed certificate.
Solution
There are two options to resolve this issue:
- Disable the option for third-party updates there entirely. (this option is NOT necessary to support third-party updates through the Lenovo Patch plugin)
OR - Choose the option to 'Manually manage the certificate'.
Either of these options will stop the Configuration Manager console from overwriting the existing certificate and allow you to keep signing updates with your custom certificate as intended.